The Kerckhoffs Principle in the Quantum Age: Why Algorithm Secrecy Fails But Key Secrecy Endures
Auguste Kerckhoffs stated that cryptographic security should depend only on the key, not the algorithm. In the quantum age, this 1883 principle is more relevant than ever.
A 140-Year-Old Principle That Still Holds
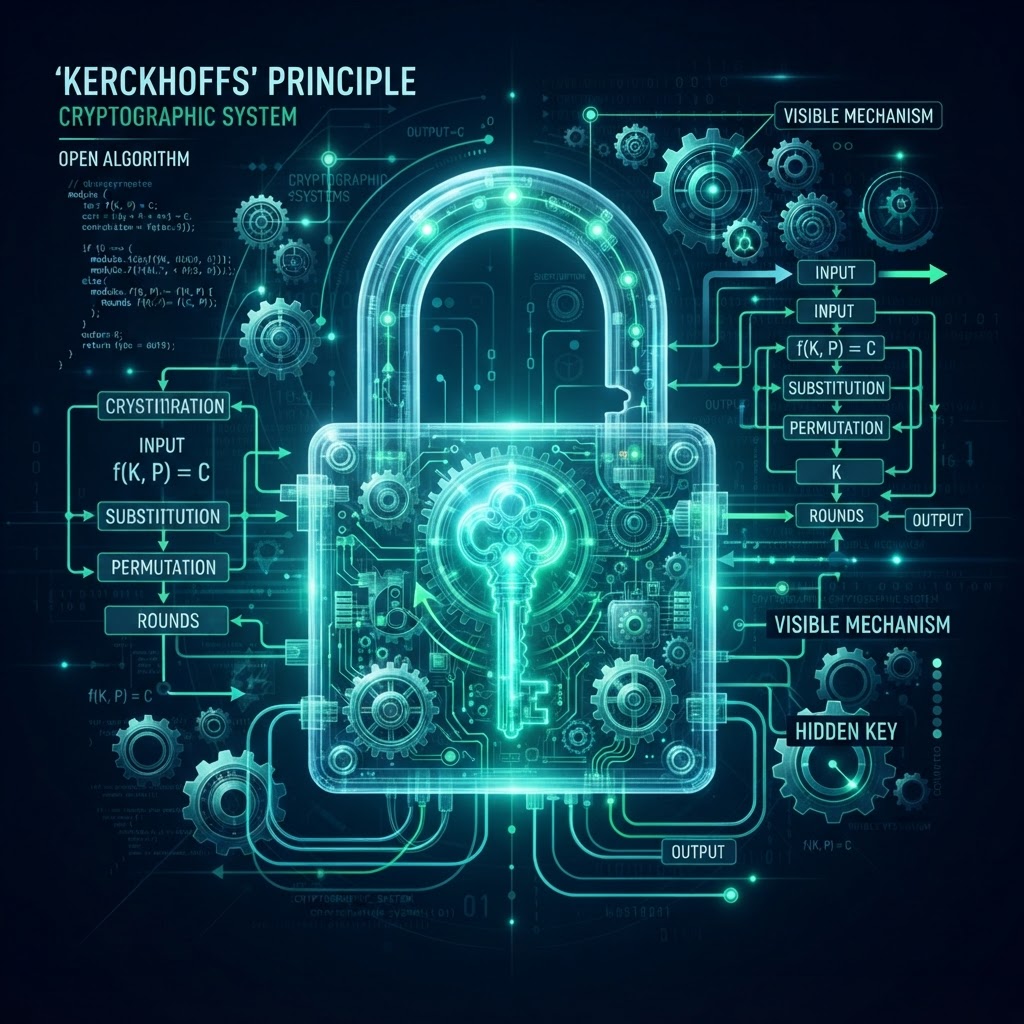
In 1883, the Dutch cryptographer Auguste Kerckhoffs published a set of principles for military cryptography in the journal Le Journal des Sciences Militaires. The most famous of these, now known as Kerckhoffs's principle, states:
A cryptosystem should be secure even if everything about the system, except the key, is public knowledge.
This principle has guided cryptographic design for over a century. It is the reason modern encryption algorithms, AES, SHA-256, RSA, are published openly. The security does not come from hiding the algorithm. It comes from the secrecy of the key.
In the quantum age, Kerckhoffs's principle is not just relevant. It is the foundation of practical post-quantum security.
Why Algorithm Secrecy Fails
The alternative to Kerckhoffs's principle is security through obscurity: keeping the algorithm secret and hoping the attacker cannot reverse-engineer it. This approach has failed repeatedly throughout history.
The Enigma machine, used by Nazi Germany during World War II, relied partly on the secrecy of its mechanism. Allied cryptanalysts at Bletletchley Park reverse-engineered the machine and broke the cipher, shortening the war by years. The Clipper chip, proposed by the US government in the 1990s, used a classified encryption algorithm. It was abandoned after researchers identified flaws in its key escrow system.
In the quantum age, security through obscurity is even more fragile. Quantum computers do not just attack keys; they can also assist in reverse-engineering and cryptanalysis. An algorithm whose security depends on its secrecy has no defense once the secrecy is lost, and quantum tools make loss of secrecy more likely.
Why Key Secrecy Endures
Kerckhoffs's principle works because the key has a property the algorithm does not: it can be changed. An algorithm is a fixed, published design. A key is a random, secret value that the user controls. If the key is compromised, the user generates a new one. If the algorithm is compromised, the entire system must be redesigned.
This distinction matters in the quantum age because quantum attacks target specific mathematical structures. Shor's algorithm breaks RSA and ECC because it exploits the mathematical structure of integer factorization and discrete logarithms. It does not break AES because AES does not have that structure. The security of AES-256-GCM depends entirely on the 256-bit key, and that key can be changed at will.
CryptShield embodies this principle. The encryption algorithm, AES-256-GCM, is a published NIST standard. The key derivation function, PBKDF2, is a published standard. The file format is documented. Everything about the system is public knowledge except the user's passphrase. And the passphrase can be changed at any time, strengthening the system without changing any of the underlying technology.
The Practical Implications
For users and organizations implementing post-quantum security, Kerckhoffs's principle has clear implications:
- Use published, peer-reviewed algorithms. AES-256-GCM has been analyzed by the world's best cryptographers for over two decades. Its security is well understood.
- Do not rely on proprietary or secret algorithms. If the algorithm's security depends on its secrecy, it has no security once the secrecy is lost.
- Focus on key management, not algorithm secrecy. The key is the one thing the user controls, and it is the one thing that determines the system's security.
- Make the key changeable. The ability to rotate keys without changing the system is a strength, not a weakness.
Key Takeaways
- Kerckhoffs's principle, published in 1883, states that a cryptosystem should be secure even if everything except the key is public.
- Security through obscurity has failed repeatedly, from Enigma to Clipper, and quantum tools make it more fragile.
- Key secrecy endures because keys can be changed; algorithms cannot, making key management the critical security factor.
- CryptShield uses only published, peer-reviewed algorithms, with security resting entirely on the user's passphrase.
Protect your data with quantum-resistant encryption
Encrypt files and text in your browser with AES-256-GCM — zero servers, zero knowledge.
Try CryptShield Now